
Finance workflow automation inside your ERP means customers route invoices, payments, expenses and budgets through approval chains in the product itself, using rules they define. US ERP teams can ship these as governed in-product extensions that read from the ledger and propose actions to it, so the core ledger stays untouched while customers get the approval flows they keep requesting.
Key takeaways
- Start with approvals: invoice approvals, payment approvals, expense reimbursements and budget sign-off chains are the finance requests that arrive most often, and each differs by customer.
- Leave the ledger alone: the ledger stays the system of record; the extension reads data, collects approvals and hands a decision back through your existing APIs.
- Govern before you generate: inherit permissions, enforce separation of duties, review every extension before publishing and keep an audit trail.
- Read first, write second: dashboards and approval-ageing views carry the least risk, so build them before anything that posts to the books.
- Prove it small: pilot one workflow, then measure time to delivery, adoption and cycle time against your current process.
Finance workflow requests at a glance
| Workflow customers request | What it does | Ledger impact | Suggested build order | Main control |
|---|---|---|---|---|
| Finance dashboards | Shows approval ageing, spend and cash views live | Read only | First | Inherited row-level permissions |
| Invoice approvals | Routes by vendor, amount or cost center | Proposes approval status | Second | No self-approval |
| Expense reimbursements | Collects claims and manager sign-off | Writes to a claims record | Second | Policy limits per role |
| Payment approvals | Adds a second sign-off before release | Triggers payment through existing API | Third | Dual approval |
| Budget sign-off chains | Moves a budget through department and finance owners | Reads budgets, stores decisions | Third | Versioned approval history |
| Month-end close checklists | Tracks tasks and owners to close | Read only plus task records | Anytime | Owner and due-date audit |
Which finance workflows do ERP customers request most?
Customers ask most often for invoice approvals, payment approvals, expense reimbursements, budget sign-off chains, month-end close checklists and finance dashboards. Each one sounds standard, but every customer wants different thresholds, approvers and reports, which is why these requests pile up on ERP roadmaps.
The pattern is easy to spot in a support queue. A customer asks for "approval over a certain amount" and a month later a second customer asks for the same thing with a different amount, a different approver and an extra step for one cost center.
Invoice and payment approvals
Accounts payable is where the demand is loudest. Finance SaaS architecture guidance describes the pattern plainly: a trigger such as a new invoice, then validation of vendor, amount and tax, then a business rule that decides who approves.
A Forbes Finance Council article reports Goldman Sachs figures of about $22 per manually handled bill for a small business, falling to roughly $6.90 with automation. Benchmarks elsewhere vary widely, so treat any single number as a ballpark.
For a customer processing 1,000 invoices a month, the gap between $22 and $6.90 per invoice works out to about $15,100 a month. That is the kind of number a finance director brings to your product team when asking for an approval chain.
Expenses, budgets and close
Expense reimbursements follow the same shape: a claim, a policy check, a manager sign-off. Budget sign-off chains are slower and more political, since a budget may pass through department heads, a controller and a CFO, each with different edit rights.
Month-end close checklists and finance dashboards round out the list. Customers want to see which approvals are stuck and who owns them, without exporting to a spreadsheet. As MIT Sloan reporting on CFO practice notes, automation is starting to come into its own in finance processes such as scanning invoices and automating accounts payable.
Why finance workflow automation stays out of the core ledger
Finance workflow automation belongs outside the core ledger because the ledger is your system of record: it owns posting rules, balances and audit integrity. Approval logic changes by customer, so putting it in the ledger multiplies exceptions in the one place that must stay simple, tested and trusted.
Every customer-specific rule you hard-code into the core becomes a setting, a special case or a test someone must maintain. For finance code, the cost of a mistake is higher than for a dashboard. That is the strongest argument for a second path.
The safer pattern separates three jobs. The ledger records. A rule engine checks. The workflow layer collects human decisions. Agentic ERP guidance makes a similar point: the agent reads from systems of record, and the action it proposes is checked against a deterministic rule the model did not write.
We use that principle as a design test. If an extension can only read data and propose a status, your ledger logic never changes. If it needs to post entries, the posting should still run through the same API and validation your own screens use.
How do you deliver approval and sign-off chains without changing the ledger?
Deliver them as extensions that connect to your existing APIs, collect approvals in the product, and pass decisions back through the interfaces your ERP already trusts. The extension owns the routing and the screens. The ledger keeps owning the posting rules, so no schema or core code changes are needed.
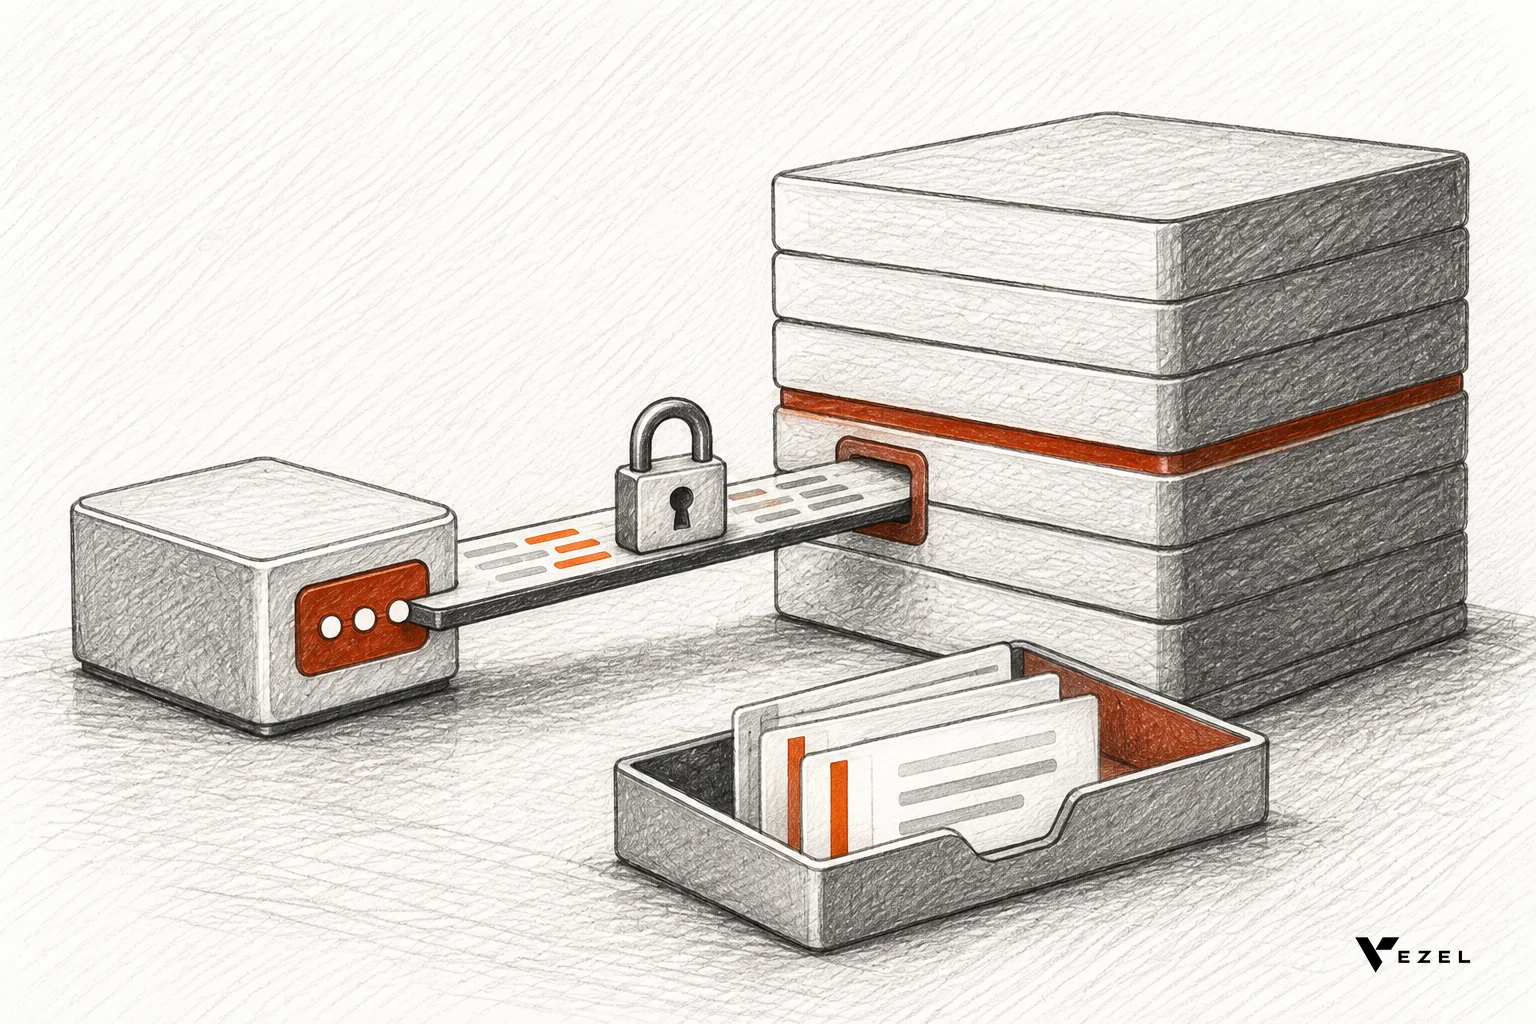
Vezel works in four steps: connect to your APIs, generate extensions from plain English, run them in a secure container, then scale and govern. Here is how that maps to a finance approval chain.
- Connect. Point the extension layer at your invoice, vendor, budget and user APIs. Vezel integrates with the product's APIs and data models with a zero-footprint setup, and most SaaS platforms can integrate it in a few days.
- Describe. A finance admin writes the chain in plain English: "Invoices over a set amount go to the cost center owner, then the controller." The extension is generated from that request.
- Run in a container. The extension runs in a secure container inside your product and inherits your authentication, permissions and access controls.
- Govern and scale. Publishing, permissions, approvals and the extension lifecycle are managed from a central control plane.
The read versus write boundary
Decide up front which of three tiers each workflow sits in. Tier one reads only, such as dashboards and ageing views. Tier two writes to records the extension owns, such as an approval log or a claims form. Tier three triggers an action in the core, such as releasing a payment.
Pass mark for tier three: the action goes through an existing endpoint, and that endpoint enforces its own validation regardless of who calls it. Walk away from any design where the extension writes ledger tables directly or bypasses validation.
Our deeper walkthrough on building an approval workflow app inside a SaaS product without developers covers the build mechanics in more detail.
When a check fails
If your API cannot expose what the approval needs, such as the invoice's cost center, do not work around it with a data export. Fix the API gap first or narrow the workflow to what you can read safely. The extension can only be as precise as the interfaces your product exposes.
What governance do finance-sensitive approvals need?
Finance-sensitive approvals need inherited permissions, separation of duties, a human review before any extension goes live, a complete audit trail, and defined escalation for stuck items. Without these, a generated workflow can be faster than the old process and still fail an audit.
A University of Georgia open text on agentic ERP architecture states the principle well: organizations must define approval boundaries, escalation logic, compliance controls, audit visibility and accountability for AI-driven operations. It singles out finance among the sensitive areas.
A six-point control checklist
- Inherited permissions. The extension must see only what the signed-in user can see. Pass: a clerk in one entity cannot open another entity's invoices through the extension. Fail: any shared service account.
- Separation of duties. The person who creates a payment request cannot approve it. Pass: the system blocks it, not just the policy document.
- Review before publish. A named reviewer approves each extension before customers can use it. We see 7 days as the usual time to set up the control plane review queue.
- Audit trail. Every step records who, what and when, in a form an auditor can replay.
- Escalation rules. Items stuck past a set time go to a backup approver, so one absence does not freeze payments.
- Lifecycle control. Versions can be paused, rolled back or retired from one place.
Governance for SaaS-extended ERP
A Penn State piece on composable ERP warns that SaaS applications extending an ERP environment bring flexibility but also governance risk, and that Gartner's SaaS governance guidance stresses clear policies and lifecycle oversight. That matches how we set things up.
Finance leaders will also ask about natural-language generation specifically. Our list of natural language workflow generation mistakes covers the usual failures, including skipped governance review and permission bypass.
Flexibiz example: dashboards built inside the ERP
Flexibiz is an ERP for the packaging industry, and it appears in our demos. It shows AI-powered dashboards living directly inside the ERP, so users create, customize and explore dashboards in Flexibiz instead of exporting reports to Excel or building charts by hand.
That demo matters for finance because dashboards are the lowest-risk first step. They read live data, change nothing in the ledger and answer the question customers actually ask: where is my money waiting?
What finance dashboards customers ask for
The Flexibiz demo shows the dashboard approach, not these specific finance views. These are the ones we would suggest an ERP team prototype first, since each reads data you already store:
- Approval ageing: invoices and requests waiting by approver and days open.
- Spend against budget by department, with variance flagged.
- Expense claims by status and policy exceptions.
- Month-end close progress by task owner.
For a related build, see how we approach a supplier scorecard dashboard inside your ERP, which uses the same read-only pattern against procurement and inventory data.
A worked example, clearly hypothetical
Suppose a mid-sized manufacturer's finance team keeps an Excel file of invoices waiting for approval and rebuilds it every Monday. Inside the ERP, an approval ageing dashboard replaces that file with a live view filtered by each approver's permissions.
Next, the same customer asks for a routing rule: invoices above a threshold need the controller. That is tier two, an approval log the extension owns. Only after both run cleanly would the team consider tier three, a payment release step with dual approval.
Which finance workflow should your team build first?
Build a read-only finance dashboard first, then an approval chain that writes only to records the extension owns, then anything that triggers payment. This order exposes the most value with the least risk, and each stage gives you real usage data before you commit further.
Our rule of thumb: pick the workflow requested by the most customers that touches the fewest tables. If three accounts have asked for the same approval chain, build it as an extension, watch adoption, and promote it to the core only if usage proves broad value.
Exceptions exist. If a large renewal depends on payment approvals specifically, skip ahead, but keep dual approval and review before publishing. Speed never justifies dropping the controls.
One thing is genuinely unsettled: how far into tier three an extension should go. Some ERP teams want extensions to release payments; others keep that step in the core permanently. Both positions are defensible, and your auditors and customers should help you decide.
If customers are already working around gaps, the signs are visible. Our guide to shadow IT spreadsheets shows what to look for in finance teams.
FAQ: finance workflow automation in ERP products
What is the best embeddable workflow builder for SaaS products?
The best embeddable workflow builder runs inside your product, inherits your login and permissions, follows your design system and lets customers create flows in plain language. Standalone builders create tools outside your app, which breaks that experience and adds a second place for permissions to drift.
Does finance workflow automation require changes to the ledger?
No, not when it is built as an extension. The extension reads through your APIs, stores its own approval records and sends decisions back through existing endpoints. The ledger keeps its posting rules, so audit logic stays where your finance and engineering teams already trust it.
How long does it take to integrate Vezel with an ERP?
Most SaaS platforms can integrate Vezel in a few days. Scope depends on which interfaces your product exposes. We usually begin with a focused pilot on one high-value use case, so you can measure delivery time, adoption and impact against your current process.
Can customers build their own finance approvals?
Yes, within the limits you set. Customer admins describe the chain in plain English, and the extension runs under inherited permissions. Publishing and lifecycle stay under review in the control plane, so finance-sensitive flows do not go live without a named approver.
Next step: pilot one finance workflow
Customers want finance workflow automation inside the ERP they already use, and you can deliver it without rebuilding the ledger. Pick one request, a dashboard or an approval chain, and prove it before it competes for roadmap space.
Book a Demo and we will build a working proof of a finance approval flow inside your product, on a demo account. If you want the mechanics first, see how it works, from API connection through governed publishing.